Instant File Search MCP Server
npm · by clayleopardlabs
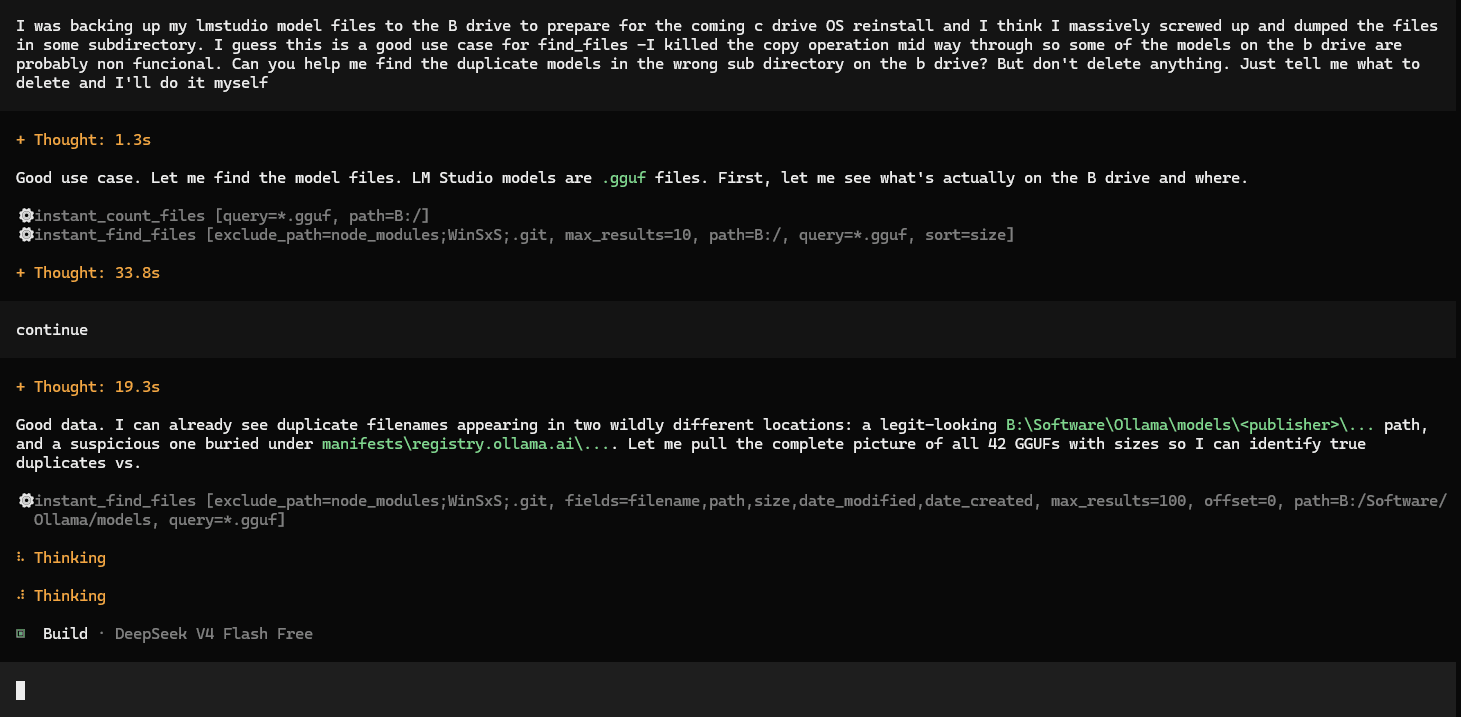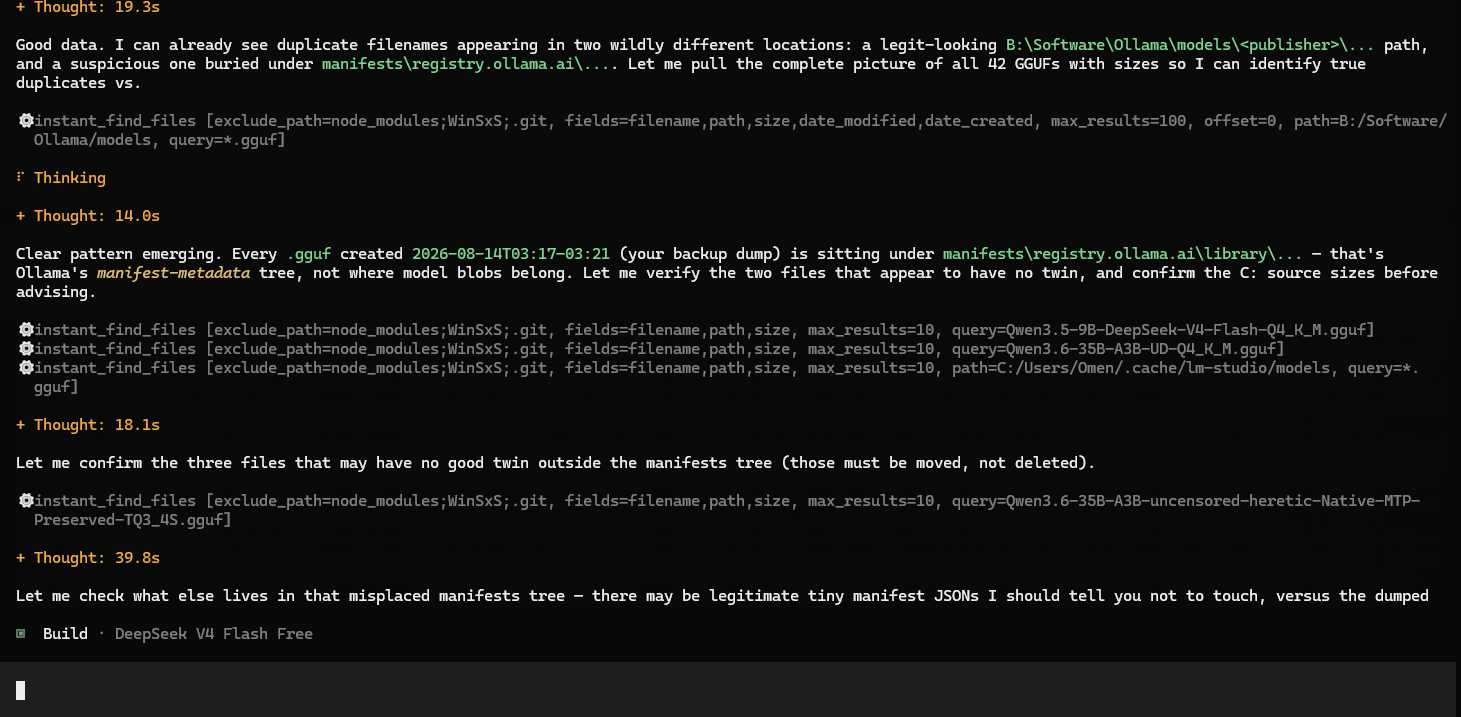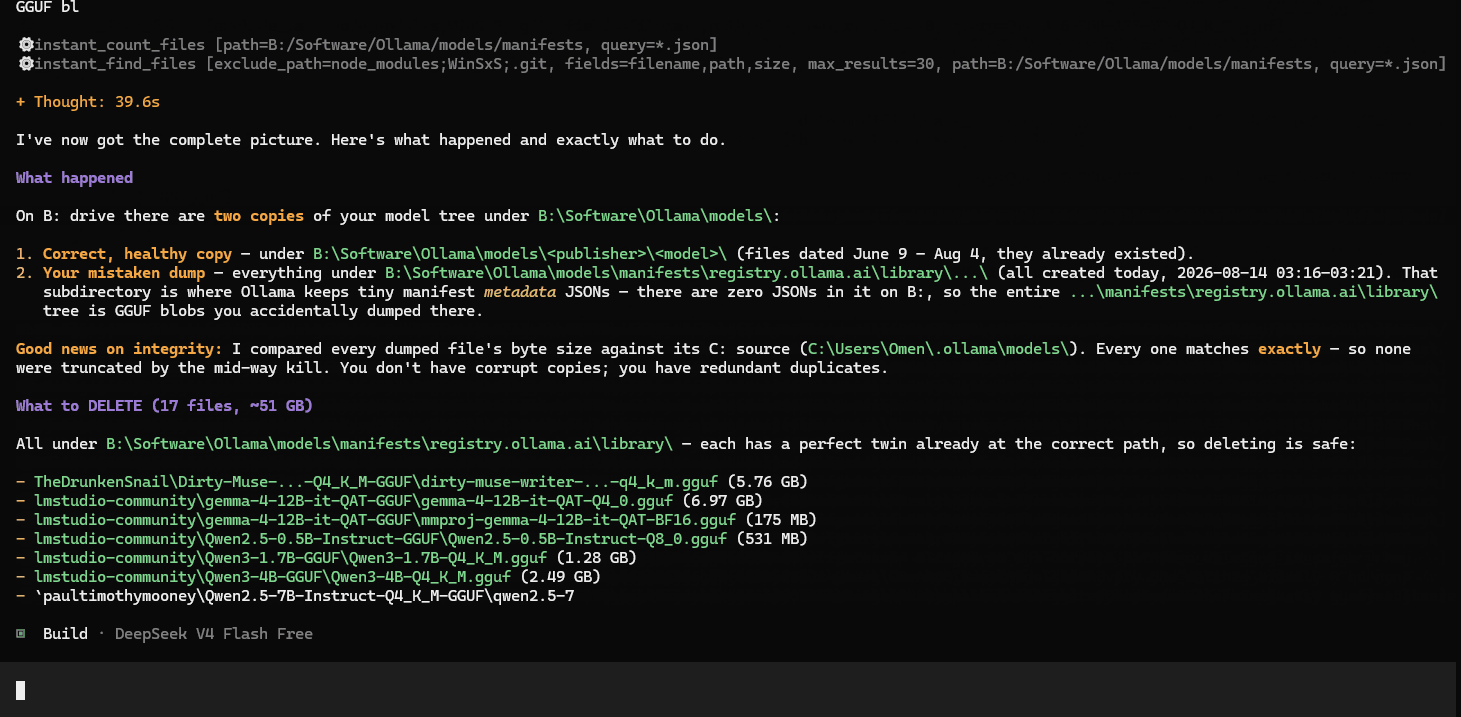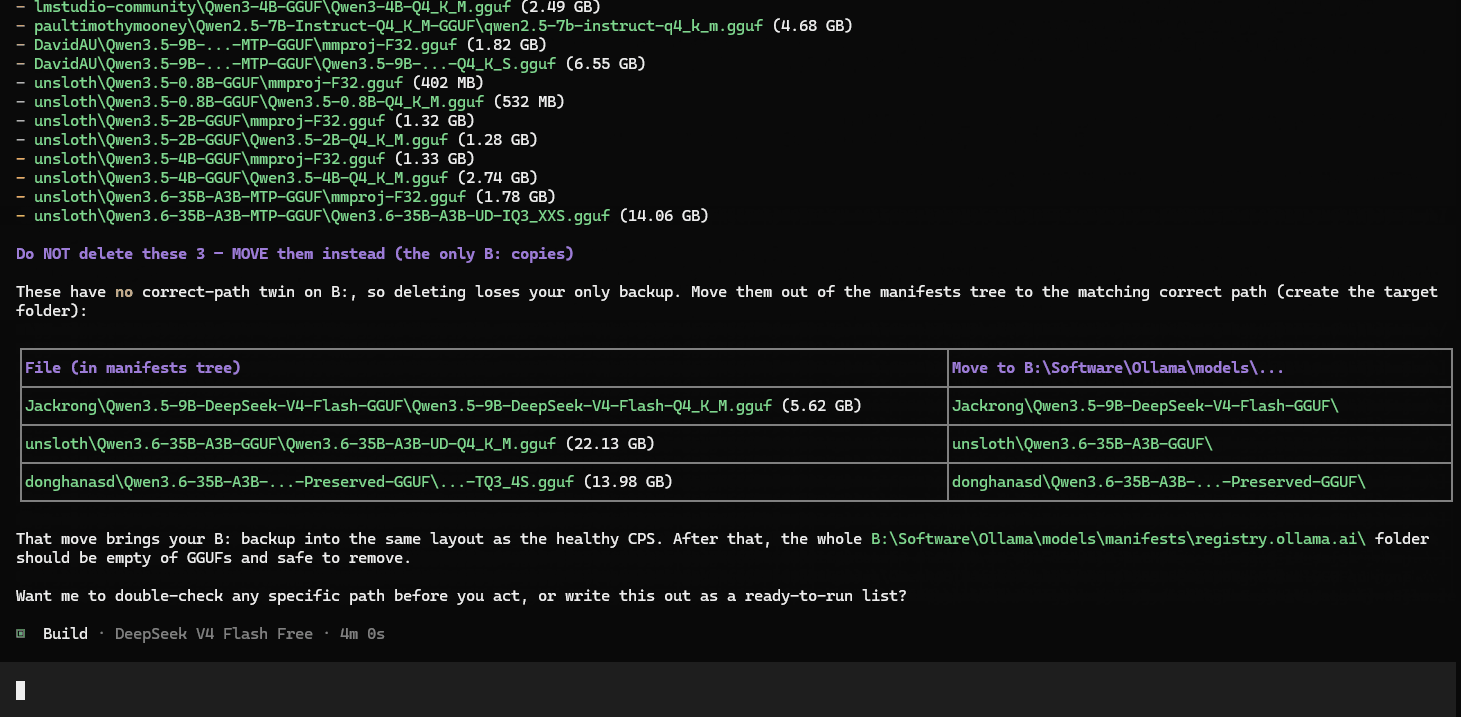
MCP server using the Master File Table to allow millions of files to be searched instantly
No known CVEs
MIT license
Actively maintained
Last commit 6d ago
Works with most clients
Transport: stdio, sse
0 tools
Grade F
MCPpedia last refreshed this data
Instant File Search MCP Server is an MCP server that MCP server using the Master File Table to allow millions of files to be searched instantly. Its tool list has not been published yet over stdio and sse, requires no API key, and scores 58/100 on MCPpedia's security, maintenance and efficiency rubric.
Step 1
Install in your client
Config is the same across clients - only the file and path differ.
CD
Supported in Claude Desktopstdio, sse · Node 18+
Paste into ~/Library/Application Support/Claude/claude_desktop_config.json
{
  "mcpServers": {
    "instant-file-search-mcp-server": {
      "args": [
        "-y",
        "npm"
      ],
      "command": "npx"
    }
  }
}
Are you the author?
Add this badge to your README to show your security score and help users find safe servers.
Embed in your READMEAbout badges →
[](https://mcppedia.org/s/instant-file-search-mcp-server)
Read me
What Instant File Search MCP Server does
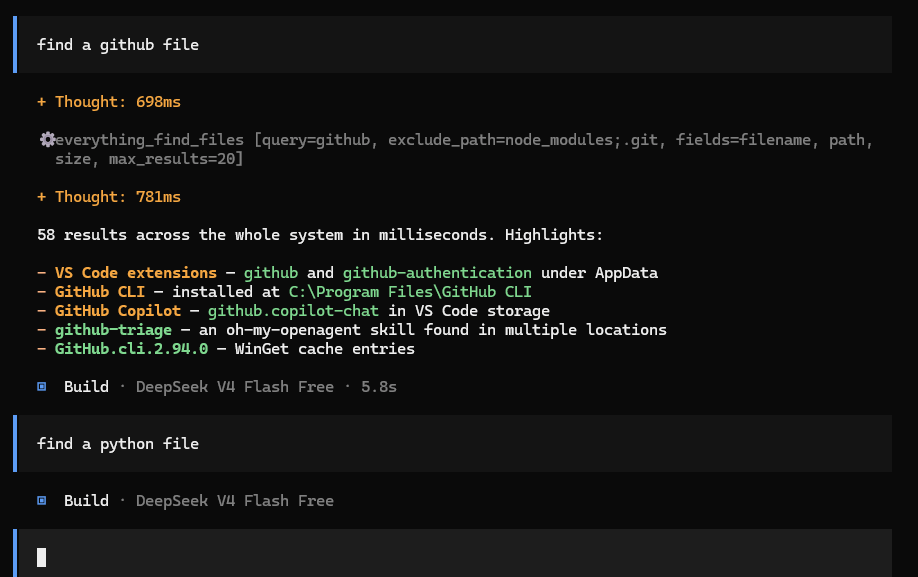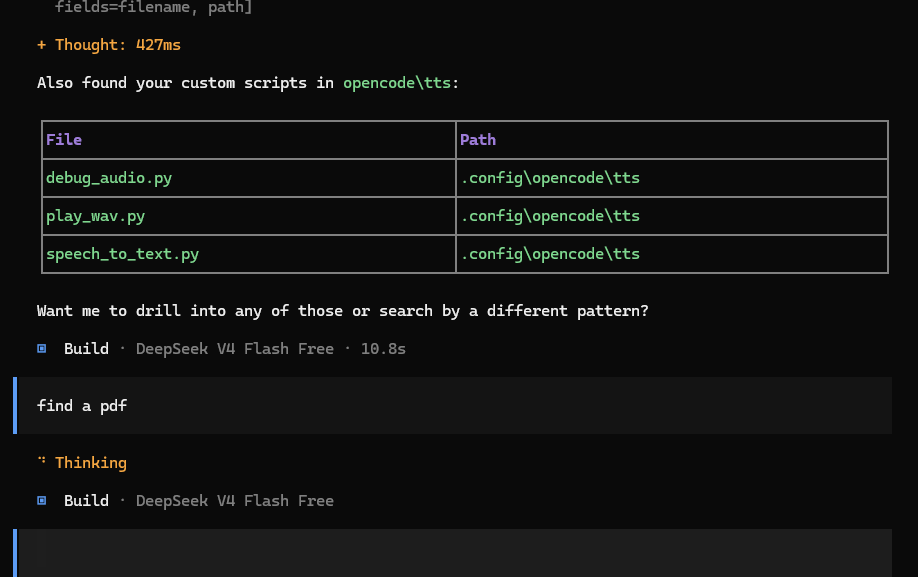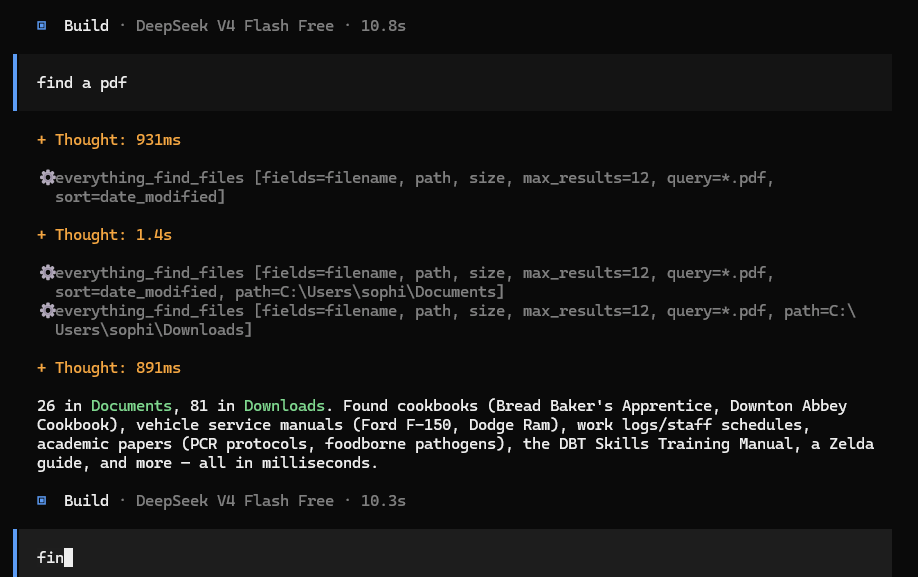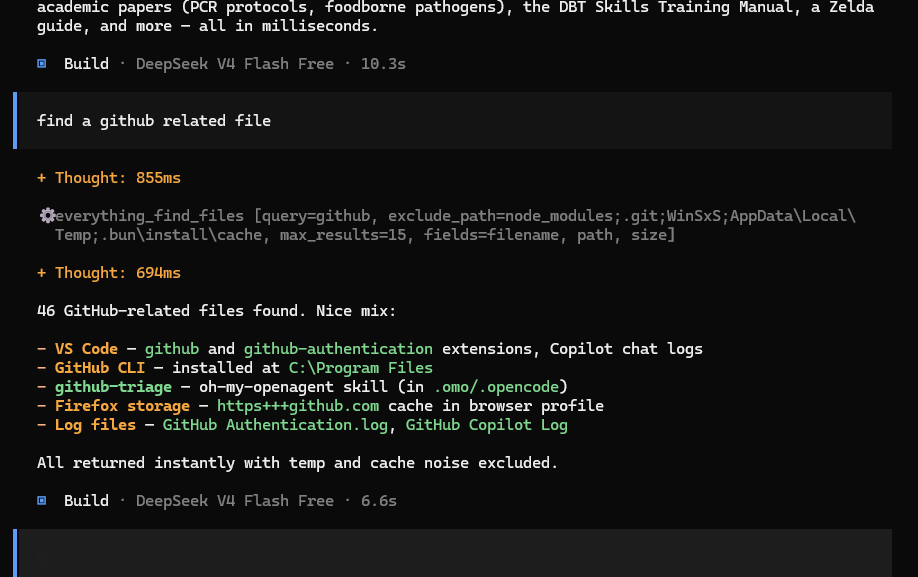
An MCP server that gives AI agents instant filesystem search on Windows. Agents can find files by name, extension, size, or date, scope searches to a directory, exclude noise folders, and count matches across millions of files in milliseconds, without walking folders one by one.
Test This Server
Run this in your terminal to verify the server starts. Then let us know if it worked - your result helps other developers.
npx -y 'npm' 2>&1 | head -1 && echo "✓ Server started successfully"
After testing, let us know if it worked:
Loading README…
Scored, not listed
Why this score
Five weighted categories - click any category to see the underlying evidence.
Score breakdown
58/100across 5 weighted dimensions
0255075100
22
12
14
10
−42
Security
Maintenance
Efficiency
Documentation
Compatibility
Categoriesclick a row to see evidence
Security
OSV.dev8 fixed
CVE-2022-29244high · fixedCVSS 7.5
Packing does not respect root-level ignore files in workspaces
### Impact `npm pack` ignores root-level `.gitignore` & `.npmignore` file exclusion directives when run in a workspace or with a workspace flag (ie. `--workspaces`, `--workspace=<name>`). Anyone who has run `npm pack` or `npm publish` with workspaces, as of [v7.9.0](https://github.com/npm/cli/releases/tag/v7.9.0) & [v7.13.0](https://github.com/npm/cli/releases/tag/v7.13.0) respectively, may be affected and have published files into the npm registry they did not intend to include. ### Patch - Up
CVE-2018-7408high · fixedCVSS 7.8
Incorrect Permission Assignment for Critical Resource in NPM
An issue was discovered in an npm 5.7.0 2018-02-21 pre-release (marked as "next: 5.7.0" and therefore automatically installed by an "npm upgrade -g npm" command, and also announced in the vendor's blog without mention of pre-release status). It might allow local users to bypass intended filesystem access restrictions because ownerships of /etc and /usr directories are being changed unexpectedly, related to a "correctMkdir" issue.
CVE-2013-4116low · fixed
Local Privilege Escalation in npm
Affected versions of `npm` use predictable temporary file names during archive unpacking. If an attacker can create a symbolic link at the location of one of these temporary file names, the attacker can arbitrarily write to any file that the user which owns the `npm` process has permission to write to, potentially resulting in local privilege escalation. ## Recommendation Update to version 1.3.3 or later.
CVE-2020-15095medium · fixedCVSS 4.4
npm CLI exposing sensitive information through logs
Versions of the npm CLI prior to 6.14.6 are vulnerable to an information exposure vulnerability through log files. The CLI supports URLs like `<protocol>://[<user>[:<password>]@]<hostname>[:<port>][:][/]<path>`. The password value is not redacted and is printed to stdout and also to any generated log files.
CVE-2019-16777high · fixedCVSS 7.7
npm Vulnerable to Global node_modules Binary Overwrite
Versions of the npm CLI prior to 6.13.4 are vulnerable to a Global node_modules Binary Overwrite. It fails to prevent existing globally-installed binaries to be overwritten by other package installations. For example, if a package was installed globally and created a `serve` binary, any subsequent installs of packages that also create a `serve` binary would overwrite the first binary. This will not overwrite system binaries but only binaries put into the global node_modules directory. This b
Community
Reviews
Be the first to review
Have you used this server?
Share your experience - it helps other developers decide.
How easy was setup?Did it work reliably?How was the documentation?
Sign in to write a review.
Frequently Asked Questions
- Is Instant File Search MCP Server safe to use?
- Instant File Search MCP Server has no known CVEs as of the latest MCPpedia security scan. Authentication requirements were not detected automatically - check the project's documentation before connecting in a shared environment. Licensed under MIT.
- How do I install Instant File Search MCP Server?
- Instant File Search MCP Server supports copy-paste install configs on its MCPpedia page for Claude Desktop, Cursor, and Claude Code. Scroll to the Quick Install section and select your client.
- What AI clients work with Instant File Search MCP Server?
- Instant File Search MCP Server is compatible with claude-desktop, cursor, claude-code. It uses stdio and sse transport.
- Is Instant File Search MCP Server actively maintained?
- Instant File Search MCP Server is actively maintained - last commit was 6 days ago.
Related
Similar servers
Others in other
I
io.github.vshulcz/deja-vu95deja-vu: local memory over the session histories of forty-three coding agents.
1.5k 6
W
MCP Wordpress Remote95MCP WordPress Remote proxy server
188 10
 Argo95
专门为 agent 打造的 agent 搜索工具,具备多语言搜索能力,覆盖中文/英文/学术/代码/购物/金融/新闻/百科。
260 1
 Football Docs94
Searchable football data provider documentation for AI coding agents. Like Context7 for football data.
228 8
MCP Security Weekly
Get CVE alerts and security updates for Instant File Search MCP Server and similar servers.
Community
Discussion
Start a conversation
Ask a question, share a tip, or report an issue.
Has anyone used this with Cursor?How do you handle auth?Any alternatives?
Sign in to join the discussion.