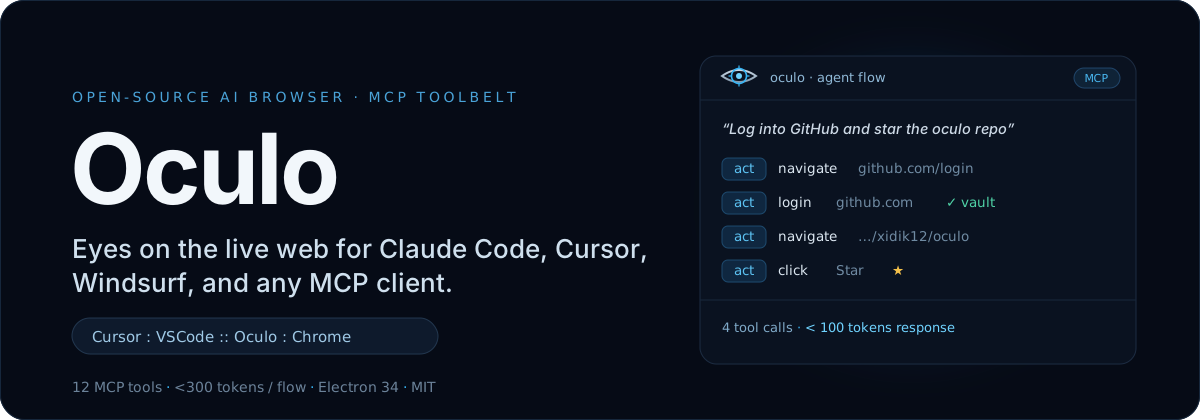
Oculo MCP Server is an MCP server that AI-powered native browser with 12 MCP tools. ~30 tokens per page. Its tool list has not been published yet over stdio, sse and http, requires no API key, and scores 79/100 on MCPpedia's security, maintenance and efficiency rubric.
Step 1
Install in your client
Config is the same across clients - only the file and path differ.
CD
Supported in Claude Desktopstdio, sse, http · Node 18+
Paste into ~/Library/Application Support/Claude/claude_desktop_config.json
{
  "mcpServers": {
    "oculo": {
      "args": [
        "/path/to/oculo/bin/oculo-mcp.mjs"
      ],
      "command": "node"
    }
  }
}
Are you the author?
Add this badge to your README to show your security score and help users find safe servers.
Embed in your READMEAbout badges →
[](https://mcppedia.org/s/io-github-xidik12-oculo)
Read me
What Oculo MCP Server does
AI-powered native browser with 12 MCP tools. ~30 tokens per page.
Test This Server
Run this in your terminal to verify the server starts. Then let us know if it worked - your result helps other developers.
npx -y 'electron' 2>&1 | head -1 && echo "✓ Server started successfully"
After testing, let us know if it worked:
Loading README…
Scored, not listed
Why this score
Five weighted categories - click any category to see the underlying evidence.
Score breakdown
79/100across 5 weighted dimensions
0255075100
30
20
15
10
−21
Security
Maintenance
Efficiency
Documentation
Compatibility
Categoriesclick a row to see evidence
Security
OSV.dev20 fixed
CVE-2026-115570high · fixedCVSS 7.4
Electron: Mitigation for compromised eMudhra intermediate certificates
### Impact A set of eMudhra intermediate certificates were compromised and are being blocked by browsers and other TLS clients. This Electron update adds the same block to both Chromium networking and Node.js `tls`, `https` and `fetch`. On earlier versions, an attacker holding a certificate issued through these intermediates and able to intercept network traffic could impersonate a TLS server to an app. Apps are only affected if they make TLS connections over a network an attacker can intercep
CVE-2026-113796medium · fixedCVSS 4.2
Electron: SameSite cookie restrictions are not applied to windows opened from links
### Impact Pages opened into a new window from a link were loaded as if the app itself had navigated there rather than the page that contained the link, so the request was treated as same-site: `SameSite=Strict` cookies were sent and `Sec-Fetch-Site` did not identify the initiating page. Content shown in the app could use this to make a credentialed top-level request to another site that relies on SameSite cookies as a CSRF defence. Apps are only affected if they load untrusted content and all
CVE-2026-113798medium · fixedCVSS 5.4
Electron: Pointer lock permission requests can be attributed to the wrong frame
### Impact For `pointerLock` permission requests made from some cross-origin iframes, `session.setPermissionRequestHandler()` was given the top-level frame's `requestingUrl` and `isMainFrame` instead of the requesting frame's. Apps that grant pointer lock based on the requesting origin could grant it to embedded content under the top-level page's identity. Apps are only affected if they embed untrusted content in iframes and decide `pointerLock` requests by origin in `setPermissionRequestHandle
CVE-2026-113797low · fixedCVSS 3.1
Electron: Extension tabs.query returns tab URLs and titles without the tabs permission
### Impact `chrome.tabs.query()` returned each tab's `url` and `title` to extensions that held neither the `tabs` permission nor matching host permissions, so any loaded extension could read the URL and title of every webContents in its session. Apps are only affected if they load extensions (`session.extensions.loadExtension`) that they do not fully trust. Apps that load no extensions, or only trusted ones, are not affected. ### Workarounds Do not load untrusted or unvalidated extensions. In
CVE-2026-114122low · fixedCVSS 3.9
Electron: Frame subscription trusts GPU-supplied frame geometry
### Impact Frame data received from the GPU process for `webContents.beginFrameSubscription` was not fully validated by the main process. A compromised GPU process could cause the main process to read out-of-bounds memory while producing the captured frame images, disclosing memory or crashing the app. Apps are only affected if they use `webContents.beginFrameSubscription` and an attacker has separately gained code execution in the GPU process. Apps that do not subscribe to captured frames are
Inventory
Tools (3)
Click any tool to inspect its schema.
~123 tokens total
Community
Reviews
Be the first to review
Have you used this server?
Share your experience - it helps other developers decide.
How easy was setup?Did it work reliably?How was the documentation?
Sign in to write a review.
Frequently Asked Questions
- Is Oculo MCP Server safe to use?
- Oculo MCP Server has no known CVEs as of the latest MCPpedia security scan. Authentication requirements were not detected automatically - check the project's documentation before connecting in a shared environment. Licensed under MIT.
- How do I install Oculo MCP Server?
- Oculo MCP Server supports copy-paste install configs on its MCPpedia page for Claude Desktop, Cursor, and Claude Code. Scroll to the Quick Install section and select your client.
- What can Oculo MCP Server do?
- Oculo MCP Server provides 3 tools: Contributing, Donate, License. See the full tools list on the server page for descriptions and parameters.
- What AI clients work with Oculo MCP Server?
- Oculo MCP Server is compatible with claude-desktop, cursor, claude-code. It uses stdio and sse and http transport.
- Is Oculo MCP Server actively maintained?
- Oculo MCP Server is less actively maintained - last commit was 117 days ago. It has 5 GitHub stars.
Related
Similar servers
Others in browser / ai-ml
 Crw95
Open-source web scraper for AI agents with scrape, crawl, and map tools
1.3k 3
 Vibe Assistant95
A cross-platform desktop application for managing AI Agents and MCP Servers. 一款用于管理AI智能体与MCP服务器的跨平台桌面应用程序。
169 3
 Codebase Memory Mcp95
Codebase knowledge graph for AI agents — 162 languages, sub-ms queries, 99% fewer tokens.
48.6k 6
 Apify Mcp Server95
Extract data from any website with thousands of scrapers, crawlers, and automations on Apify Store ⚡
16.1k 1
MCP Security Weekly
Get CVE alerts and security updates for Oculo MCP Server and similar servers.
Community
Discussion
Start a conversation
Ask a question, share a tip, or report an issue.
Has anyone used this with Cursor?How do you handle auth?Any alternatives?
Sign in to join the discussion.